ChatGPT Wallet and the Moment AI Agents Enter the Payment Stack
OpenAI’s ChatGPT Wallet is more consequential than another frontier-model release: it connects an AI agent to a constrained, auditable payment rail, making delegated commerce an architectural and regulatory problem rather than a demo.
 Lukas Hoffmann🇩🇪 Europe & Frontier CorrespondentNov 13, 2026 10m read
The important development is not another model release
The most significant Western AI-lab development between 26 October and 13 November 2026 was OpenAI’s 13 November launch of **ChatGPT Wallet**↗. That judgement needs a little discipline. In any two-week period, frontier labs can announce faster inference, larger context windows, better tool use, or a new benchmark lead. Such releases matter, but they normally improve an already familiar category: the model as a service.
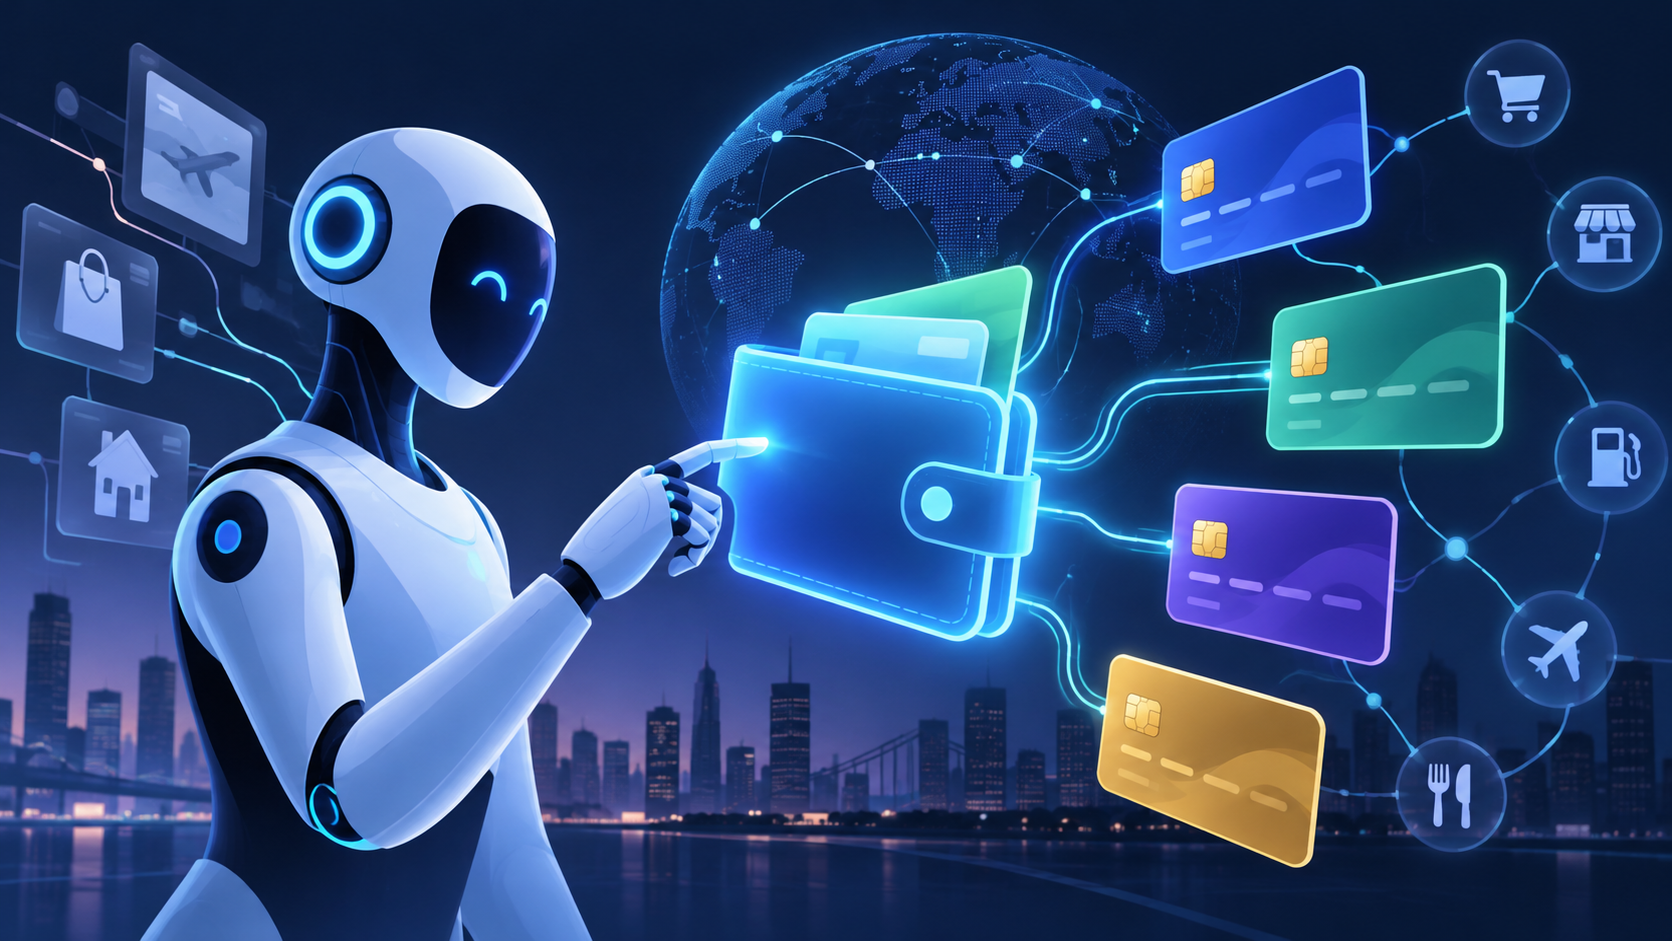
ChatGPT Wallet changes a boundary instead. It connects an agent to the payment stack—the part of the internet in which decisions create binding economic consequences. The product is initially narrow: it is rolling out to eligible US ChatGPT Pro users, aged 18 or older, using eligible US-issued cards, and it is used within conversations with a user’s designated “dot,” rather than ordinary ChatGPT threads. The launch is therefore not evidence that autonomous consumer commerce is solved. It is evidence that OpenAI has begun to construct the trust infrastructure required for it.
That distinction is decisive. An agent that can research, recommend and populate a cart is useful. An agent that can cause a card-authorised order to be submitted must answer harder questions: whose intent was represented, what exactly was approved, which party saw credentials, who can contest an error, and how does a merchant distinguish a legitimate delegated action from automation abuse? The Wallet is OpenAI’s first visible answer to those questions at payment-rail level.
The strategic unit is not the chatbot session. It is the chain of authority from a human instruction to an auditable financial outcome.
OpenAI’s choice of partners—American Express, Mastercard and Visa—also matters. It signals that this is not an attempt to replace card networks with an AI-native closed loop. It is an attempt to let agents operate through existing network rules, issuer relationships, rewards and dispute mechanisms. In European terms, this is a characteristically pragmatic architecture: add a new delegation layer, but preserve the regulated and operationally mature layers underneath it.
A constrained transaction architecture
Tokenisation separates intelligence from credentials
The central design decision is credential separation. A user enrols a card through a dedicated secure flow; according to the Wallet help documentation↗, OpenAI does not receive the complete card number or security code in ordinary chat. When the user approves a purchase, the payment network issues a transaction-specific token—a substitute card number with its own expiry and security code—to complete that payment.
This is more than a familiar security flourish. It establishes an important division of labour:
- The agent can plan a purchase and prepare a checkout, but does not need durable access to the primary account number.
- The payment network and issuer retain the card-authorisation role and can apply their established controls.
- The merchant receives a payment credential sufficient for the specific transaction, rather than the consumer’s permanent card details.
- The user remains the source of approval and retains the card relationship, including applicable rewards and dispute protections.
A good architecture removes privileges rather than merely promising good behaviour. This one aims to ensure that an agent compromise cannot automatically become a permanent credential compromise. That does not eliminate fraud, obviously. A token can still be used in the wrong transaction if authorisation or checkout state is manipulated. But the blast radius is smaller than in a design where a general-purpose assistant stores reusable payment credentials in its own working environment.
The approach sits alongside the earlier Agentic Commerce Protocol work with Stripe↗ and the published Delegated Payment Spec↗. Those materials make a second design principle clear: OpenAI is not positioning itself as the merchant of record. The seller keeps responsibility for price, inventory, fulfilment, returns and customer service. This is strategically sensible. It avoids trying to centralise product liability and operational delivery inside the model provider, while giving merchants a route to accept agent-mediated intent.
Explicit approval is the product’s real safety feature
At launch, each purchase requires a review of the merchant, items, quantities, total price and selected card, followed by a biometric security check on a supported device. Face ID or fingerprint confirmation is not merely friction. It is the point at which a conversational recommendation becomes a user-authorised transaction.
That review creates three things that autonomous agents otherwise lack:
1. a visible representation of the specific scope of consent; 2. a durable record that the customer approved a particular merchant, amount and basket; and 3. a practical opportunity to detect an agent error before payment execution.
The scheme resembles the logic of dynamic linking in European payment authentication: consent should attach to a payee and amount, not to an abstract invitation for software to spend money. The European Banking Authority’s SCA framework↗ was written before today’s consumer agents, but its principle travels well: an authentication event is meaningful only when it is bound to the transaction the person believes they are authorising.
OpenAI has described a future in which users may establish limits by category, amount or time. That is the genuinely difficult next phase. Per-purchase biometric approval is a controlled pilot. Delegated recurring authority requires a policy engine: machine-readable mandates, allowed merchants, product substitutions, budget ceilings, revocation, anomaly detection, and a clear answer when the model interprets a natural-language instruction too broadly.
“Buy the usual detergent if it is good value” is not a payment instruction until a system can define “usual,” “good value,” acceptable substitutions and the maximum authorised exposure.
Merchant adoption is an identity-and-risk problem
The technical bottleneck is not only payment. A web agent using a cloud browser can look like a scraper, bot or account-takeover attempt to a merchant’s anti-fraud system. This is why the accompanying Commerce Partner Playbook and merchant guidance are almost as consequential as the wallet itself.
OpenAI says Wallet can operate with existing checkout forms, while merchants can also improve acceptance through recognised signed agent traffic, current product feeds and integrations with payments and fraud vendors. The documentation around the commerce production flow↗ describes the operational side of this change: authoritative checkout state, order updates and payment hand-off cannot be inferred reliably from a fluent natural-language exchange.
The merchant must remain able to say no. It needs to determine whether the request is from a real authorised customer, whether stock and price are current, whether a basket changed after approval, and whether the transaction triggers its own risk policies. Agentic commerce will therefore depend on verifiable agent identity and high-quality state synchronisation—not on prose prompts alone.
Regulation catches up with delegation
Europe: consent, SCA and liability come first
The EU already has a useful vocabulary for analysing the Wallet even though its payment rules do not name “dots.” Under the current PSD2 framework and the proposed PSD3/Payment Services Regulation package, the important concepts are payment-service authorisation, strong customer authentication, fraud controls, data protection and allocation of liability. The European Commission’s payment-services package↗ is explicitly aimed at a more harmonised retail-payments market with stronger protection against modern fraud.
For an AI agent, the key regulatory question is not whether it is clever. It is whether its actions are within valid payer consent. Initial Wallet design is comparatively legible because it keeps a human confirmation immediately before execution. A model’s mistaken product comparison may be annoying; a purchase approved after the user sees the final basket is easier to classify and contest than a silent transaction produced by a broad standing instruction.
The harder case is pre-authorised autonomy. European rules make this a demanding design task because remote authentication must be related to the particular payment. The Commission’s proposed reforms also emphasise Verification of Payee, fraud information sharing and additional consumer protections. For future agents, those obligations point toward narrowly scoped mandates and clear warnings, rather than an expansive “let my assistant handle it” toggle.
The EU AI Act adds a separate but complementary lens. A consumer-facing agent must be transparent that it is AI, while high-risk determinations such as creditworthiness carry more substantial obligations. Even where a shopping agent is not a high-risk AI system, the payment context intensifies expectations around logs, human oversight, cybersecurity and data governance. The agent’s model may be operated in one company, the wallet in another, the issuer in a third and the merchant in a fourth. Responsibility cannot disappear into that supply chain.
The United States: consumer redress is the stress test
In the United States, the architecture will be tested against consumer-protection rules, card-network dispute processes and supervision of payment platforms. The CFPB’s digital-wallet and payment-app supervision rule↗ captures the policy direction: a technology company does not escape financial-services scrutiny because it describes itself as a software platform.
Two questions will matter in any incident:
- Was the transaction genuinely authorised, and what evidence demonstrates that authorisation?
- Did the responsible parties provide effective dispute, refund and support mechanisms when the agent, merchant interface or fraud controls failed?
- Was transaction and behavioural data used only as needed to operate the service, or repurposed into a surveillance and targeting asset?
OpenAI’s privacy notice and the product design claim that raw card credentials remain outside the agent and that wallet data is not sold or used for cross-context behavioural advertising. Those are welcome boundaries, but transaction data remains exceptionally sensitive: it reveals preferences, health-adjacent purchases, travel, household patterns and economic circumstances. Tokenisation protects payment credentials; it does not by itself solve transaction-data governance. Retention limits, access controls, purpose limitation and meaningful deletion paths will be central to trust.
Why this has greater long-term significance than a benchmark gain
The control point moves toward the agent interface
If AI agents become a routine entry point for shopping and bookings, the interface that interprets user intent may become as strategically important as search ranking, app stores or browser defaults. The agent can influence discovery, comparison, cart construction and the moment of checkout. A payment capability turns that influence into a potential commerce control point.
That does not mean OpenAI has won commerce. Merchants can refuse access, networks can impose rules, issuers can decline transactions, and users can choose other assistants. Moreover, OpenAI says it is not taking a transaction cut at launch. But the decision not to monetise immediately should be read as infrastructure strategy, not altruism. First establish trusted routing, merchant compatibility and recurring user behaviour; only later decide which layer—subscriptions, merchant tools, advertising restrictions, analytics or payments services—captures value.
The near-term competitive implication is that every major assistant provider now needs a credible answer to three linked questions: identity, authorisation and settlement. Better reasoning is no longer sufficient for agents that claim to complete real-world tasks. The winning systems will combine model capability with constrained permissions, reliable tool execution and a redress path that customers understand.
The correct measure is not autonomy, but controllable delegation
There is a tendency to measure progress by how little human intervention remains. In payments, that is the wrong objective. The relevant metric is whether a user can grant authority that is specific, reversible, inspectable and proportionate to the risk.
OpenAI’s launch is important precisely because it begins with a restricted form of delegation. It keeps the human in the loop, reuses mature network protections, limits credential exposure and leaves merchants in their established role. Its limitations—US-only availability, Pro gating, eligible cards and per-transaction biometric approval—are not signs of failure. They are an acknowledgement that financial agency should expand slower than model fluency.
For now, ChatGPT Wallet is a tightly bounded system, not a general autonomous purchasing mandate. But it supplies the architectural template for the next contest in AI: not who can produce the most persuasive answer, but who can take action in the economy while remaining secure, accountable and governable. That is why the 13 November announcement deserves more attention than another transient movement in the model leaderboard.
Links & Resources
External links — opens in a new tab
🇩🇪 Europe & Frontier Correspondent · Berlin, Germany
Covers the European labs and the frontier research redrawing the field.
Artificial Intelligence: Origins and Developments
by Richard Murdoch Montgomery
A comprehensive survey of AI from Turing machines to deep learning — neural networks, expert systems, and the philosophical debates that shaped the field.
Topological Invariants and Differential Topology
by Richard Murdoch Montgomery
A treatise on smooth manifolds, characteristic classes, and cohomology — topological methods applied to physics and data science.
The HP 17BII Financial Calculator
by Richard Murdoch Montgomery
A 50-chapter treatise integrating financial mathematics, business reasoning, and Solver-based modeling — from annuities to investment analysis.
The TI-84 Plus C Silver Edition
by Richard Murdoch Montgomery
A 609-page volume covering arithmetic, algebra, graphing, calculus, statistics, and programming on the TI-84 Plus C Silver Edition.
Comments
Open discussion — no account needed. Be respectful.
More from Western AI Desk
Anthropic’s IPO Roadshow Turns Frontier AI into a Public-Market Test
Anthropic’s proposed IPO combines a vast primary offering, a $26 billion strategic placement and an unusual mission-control architecture. The roadshow tests whether public markets will finance frontier AI’s extraordinary infrastructure burden without obtaining conventional shareholder control.
Lukas Hoffmann
Anthropic’s Fable 5.2 Is a Bid to Make Frontier AI an Enterprise Utility
Anthropic’s November model release is more than a benchmark push: it is an attempt to turn expensive, long-running AI agents into a managed enterprise product, with safety access and task economics as the moat.
 Sarah Brennan
Agents, APIs, and an IPO Clock: Anthropic's Claude Duet, OpenAI's Decisions API, and the Week's Capital Moves
Anthropic launched Claude Duet, a proactive background agent built on Opus 5.5, the same week OpenAI's Decisions API reached general availability — two very different bets on what enterprise AI infrastructure should look like. Meanwhile, OpenAI is closing in on a $30 billion raise at a $1.25 trillion valuation, and Anthropic's own IPO clock is ticking toward November.
Sarah Brennan